Website Security Services.

Know who has access.
Know what happens next.
An unfamiliar administrator, a security warning or an abandoned plugin can leave a business owner unsure who should act. C3i3 provides website security services focused on the agreed website controls, access review, maintenance coordination and recovery responsibilities, with a clear record of what needs attention.
This is practical website support, not a claim that every threat can be prevented. We review the site and provider boundaries, identify the controls relevant to the platform and agree the work your business is commissioning. Access, configuration, software upkeep and recovery are considered together because an unclear handover can undermine an otherwise sensible setup. If the situation requires incident response, forensic investigation or a wider security specialist, we identify that boundary rather than present ordinary website support as a substitute. Your business retains decisions about risk, account ownership and any required specialist involvement.
A clear account and access picture
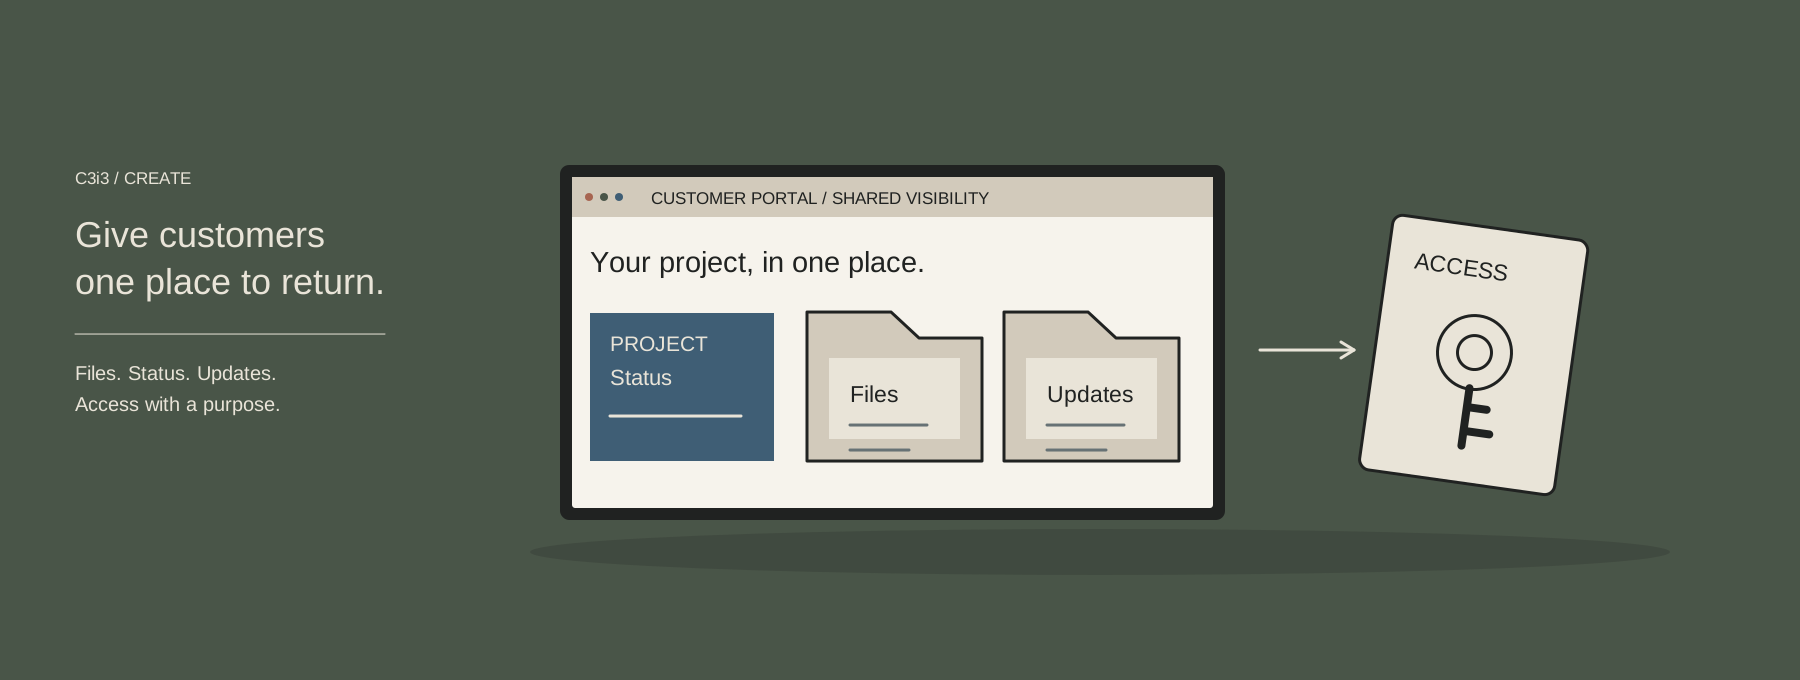
Identify the business owners, provider access and recovery contacts for the agreed website services.
A prioritized website-control review
Separate observed configuration and maintenance issues from assumptions and work outside the website support boundary.
An understandable escalation route
Record who acts on a warning, which provider controls the affected service and what the business must decide before work proceeds.
Clear responsibilities.
Useful ongoing work.
Your written scope confirms the depth and final format of the work. These are the components we can bring together for website security services.
- 01Website and provider boundary map
Document the agreed website platform, host, domain services, administrative accounts and connected tools. Identify where C3i3 can make a change and where the host, email provider or another specialist must act. The review follows the commissioned systems rather than an undefined promise to secure the entire business.
- 02Administrative-access review
Review named administrator accounts, roles, former-provider access and available recovery routes. Recommend or carry out approved access changes with the business owner. Keep secrets in the appropriate private system; a shared review document records responsibility and status rather than passwords or recovery codes.
- 03Relevant configuration checks
Review the agreed platform and hosting controls, such as available authentication settings, certificate status and account permissions. Document the specific finding and proposed action. We distinguish controls that are present from those actually configured and checked for the relevant account or site.
- 04Software and dependency priorities
Connect the security review to the maintenance inventory and available update information. Flag components that need updating, replacing or further investigation. Work involving custom code or unsupported dependencies receives a defined next step instead of being hidden inside a general security status.
- 05Recovery and response responsibilities
Identify available copies, restore access and the provider responsible for recovery. Agree the initial route for reporting a warning or suspected incident. Record any coverage limits and specialist dependencies so a business owner does not discover an emergency-response gap during the incident.
- 06Findings and approved-change record
Provide a prioritized record of observed issues, approved changes, verification and remaining responsibilities. Each open action has a business or provider owner. The record explains what was reviewed and what was outside scope, rather than implying that a checklist certifies complete security.
Bring the right
specialist into the work.
This work connects to the related website, content, and operational support below. Explore the relevant service to see its distinct scope and deliverables.
Website Management
Website management gives the ongoing tasks on your site a clear owner and a practical plan. We coordinate the agreed updates, maintenance, checks, and improvements so you know what is being handled, what needs approval, and what comes next.
Explore website managementWebsite Maintenance
Website maintenance handles the agreed technical upkeep of an existing site. We review its platform and dependencies, plan appropriate updates and checks, and document the recovery and provider responsibilities that support the work.
Explore website maintenanceA clear process.
An accountable team.
The work follows the business priorities, agreed capacity, responsible people, and review process. Open each step to see what happens and what it produces.
01Establish the situation and boundaries.
We identify the platform, providers, current warning or concern and the website work required. A suspected active incident is treated separately from a routine controls review so evidence and specialist needs are considered appropriately.
A review brief, access requirements and escalation boundary.
02Review the agreed controls.
We examine the named systems and document the actual access, configuration, maintenance and recovery findings. Findings distinguish an observed issue from a recommendation or an unanswered question that requires a provider.
A prioritized findings record with proposed owners and actions.
03Apply approved changes.
We carry out the commissioned website changes or coordinate the responsible provider. Access and other sensitive changes follow business authorization, with relevant function checks and a record of what changed.
A change and verification record for the agreed work.
04Hand over the next responsibilities.
We explain unresolved items, recovery dependencies and when the business should involve another specialist. If ongoing review is commissioned, the next work follows the agreed coverage and the platform’s actual needs.
A website-controls register and a practical follow-up plan.
A former supplier still has administrator access.
In an illustrative inherited website, the owner cannot tell which administrator accounts belong to the current team. The useful task is to identify the business account owners, verify the access still required, agree changes and check that authorized work can continue. The review also records recovery contacts and provider responsibilities. This is an example of access housekeeping, not a claim that removing an old account proves the website has never been compromised.
| The question or stage | What we examine | Why it matters |
|---|---|---|
| Ownership | Business account holders and recovery contacts | Make account control usable beyond one employee or supplier. |
| Access | Named users, roles and continuing need | Approve changes using actual responsibilities rather than guesswork. |
| Change | Authorized removals or permission adjustments | Keep the business and current providers able to perform their work. |
| Record | Completed actions and unanswered questions | Leave a clear follow-up when a provider or specialist must investigate. |
To show how website security services can support a decision. Your support plan and priorities depend on the actual systems, workload, people, and constraints in your brief.
Agree the priorities.
Then scope the support.
Scope names the website and accounts reviewed, controls covered, approved changes, review record and provider coordination. It does not automatically include managed detection, continuous monitoring, penetration testing, legal compliance certification, forensic investigation or emergency incident response. Malware cleanup and restoration are separate unless expressly included. We agree coverage and escalation contacts before ongoing support begins. If there is an active warning, describe what you observed and when, without sending passwords or sensitive logs in a public enquiry.
| Before we start | What we agree |
|---|---|
| The decision | The business priority, current systems, support need, and boundaries the work needs to address. |
| The deliverables | Management and delivery scope, format, review rounds, responsibilities, and handover. |
| The investment | Written fees, schedule, dependencies, and any separate third-party or implementation costs. |
We confirm the proposal before work begins. You can commission a focused improvement, agree an ongoing support plan, or connect specialist work to a broader service.
Discuss scope and timingUseful questions.
Straightforward answers.
Can you guarantee that our website will not be hacked?
No. The service addresses defined website controls and maintenance responsibilities. Software, hosting, user behavior and outside services all affect exposure. We describe the work and its limitations rather than make a guarantee that no incident can occur.
Is this a security audit or a compliance certificate?
It is a scoped website-control review and approved support work. Any formal audit, compliance assessment or independent test needs its own specification and qualified provider. We do not describe a routine configuration review as certification.
What if we think the website is already compromised?
Tell us the visible symptoms and relevant timing so the response boundary can be assessed. An active incident may need the host or a security-response specialist. We agree the appropriate route before making changes that could affect investigation or recovery.
Can you remove access for former employees or suppliers?
Approved access changes can be included when account ownership and authority are established. We review what each account controls and preserve the necessary business access. Credentials and recovery details are handled through an appropriate private process.
Does our hosting company already cover this?
The answer depends on the hosting agreement. Hosting security, website software, administrator accounts and connected tools can have different owners. We map those responsibilities and identify a task that remains uncovered rather than assume the host covers everything.
Do you provide round-the-clock emergency response?
Coverage is defined in the written agreement. Routine website security support should not be interpreted as continuous monitoring or round-the-clock incident response. If your business needs that coverage, it needs an explicitly suitable response arrangement.
Can this connect to ongoing maintenance?
Yes. Access findings, configuration decisions and software priorities can inform the maintenance work. We keep a shared responsibility record so security-related tasks do not become a second, disconnected list with no clear owner.
Will you need unrestricted access to all our systems?
No. Access should match the commissioned website work. We identify the accounts and permissions required, use appropriate authorization and document provider boundaries. A website support engagement is not permission to inspect unrelated email, employee records or other business systems.
Keep the ongoing work
connected.
For a related perspective, explore what to do when a business website looks hacked. Or return to all Manage services.